Why insurers are still running on legacy systems
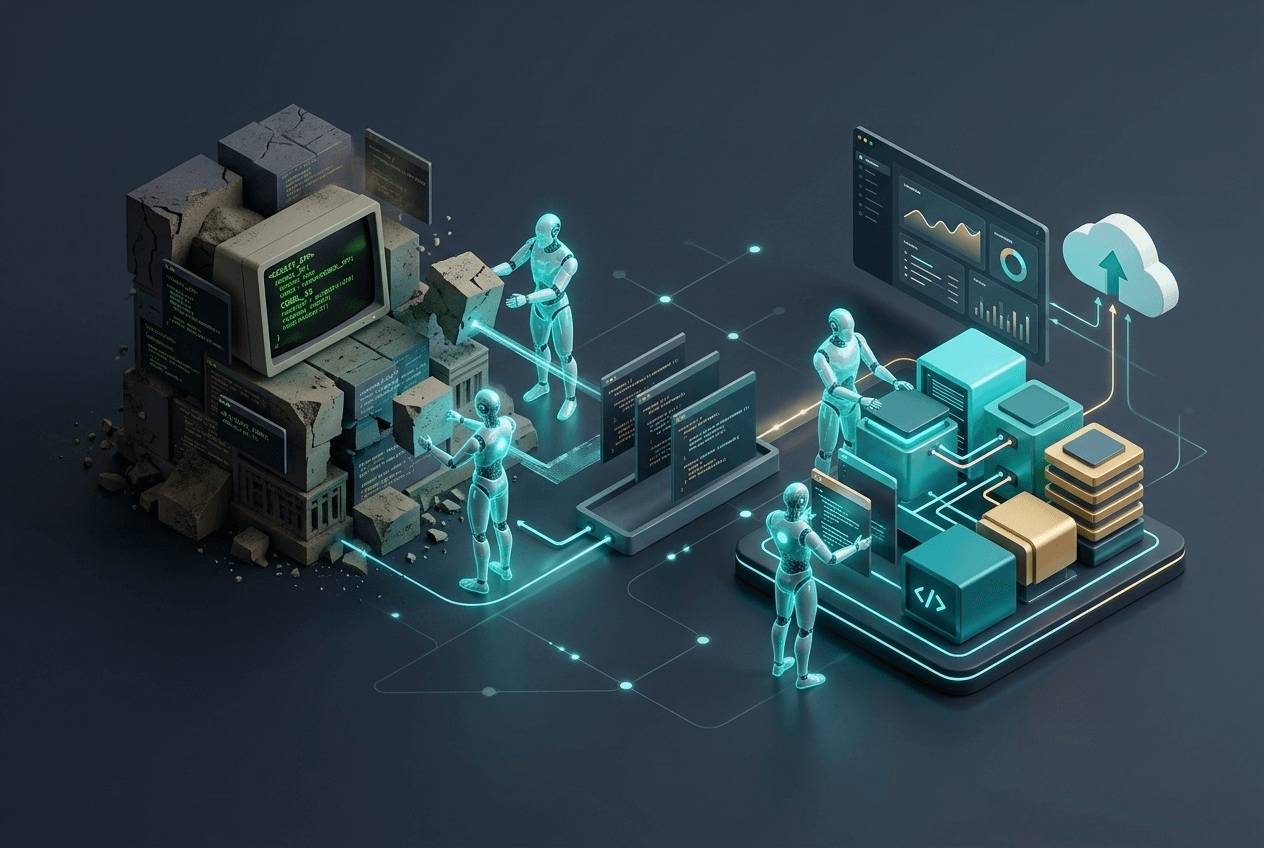
Many insurers still run their core business on systems built decades ago. Policies are issued, billed, and renewed on mainframes running COBOL, a programming language from the late 1950s. These systems are reliable, but they're hard to change. That's why insurance legacy modernization keeps rising on CIO agendas, and why insurance cloud migration is usually how it happens.
The pressure comes from three sides. The people who know these systems are retiring. Launching a new product can take months because the rules are buried in old code. And nightly batch runs mean data is often a day old, which slows down pricing, claims updates, and any AI project that needs fresh data.
The usual mistake is trying to move everything at once. Replacing all the core systems in one go often runs late and over budget. A better plan treats each system differently, moves the safest pieces first, and keeps policies running the whole time.
Policy, claims, and underwriting systems each need a different plan
A policy administration system is the core software that creates, changes, renews, and cancels insurance policies. It holds each policy's terms, coverage, and premium history, and it feeds billing, claims, and reporting. Because everything depends on it, it's usually the hardest and riskiest system to move.
Claims systems change more often. New channels, fraud checks, and faster payouts all need quick updates. Claims also gain the most from the cloud's ability to scale up during storms and other spikes. Many insurers move claims early, either to a modern cloud claims product or by rebuilding it in stages.
Underwriting sits in between. Its rules and rating logic change often and work best as small, separate services that pricing and AI tools can call. The core risk data, though, may stay tied to the policy system until that moves too. Map how these three systems share data before you choose a move for any of them.
What to move as-is, what to rebuild, and what to leave alone
Insurance cloud migration has five main options. Rehost moves a system as-is, often called lift and shift. Replatform moves it with small changes, like switching to a managed database. Refactor rebuilds it for the cloud. Retain keeps it where it is for now, and retire switches it off. Most insurers end up using all five.
The right move depends on the workload, not on how old the system is.
Workload | Best move | Why |
Reports, data warehouse, document archives | Rehost or replatform | Low risk, quick wins, cheaper storage |
Underwriting rules and rating | Refactor | Changes often, and pricing and AI tools need to call it |
Claims | Replace or refactor in stages | Must scale up during catastrophe spikes |
Active policy administration | Move one product line at a time | Too risky to move in one go |
Closed books (policies no longer sold) | Retain or retire | Few changes, so moving them rarely pays off |
Mainframe batch jobs | Replatform or rewrite gradually | Tools can convert old code, but every result needs testing |
Lift and shift vs refactor isn't an either-or choice. Rehosting gets a system off old hardware fast, but it brings the old problems along. Refactoring fixes them but takes longer. A common path is to rehost first to meet a data center deadline, then refactor the parts that change most. A migration that moves in stages, with a rollback plan at every cutover, keeps either approach safe.
Regulatory limits that change an insurance cloud migration
Insurance regulators allow the cloud, but the insurer stays responsible for its data wherever it's stored. So before moving, insurers check each cloud provider's security. Their contracts should say how fast the provider reports a breach and where the data is stored. They also need a way to get their data back and switch providers if needed.
In the US, each state regulates its own insurers. New York's regulator, the New York State Department of Financial Services (NYDFS), has some of the strictest rules. Since November 2025, insurers licensed in New York must use multi-factor login on every system and keep a written list of all their systems. NYDFS has also said that using a cloud provider doesn't shift the insurer's compliance duties to that provider. Many other states follow a similar set of rules: the National Association of Insurance Commissioners (NAIC) data security model law. It also asks insurers to check their vendors' security.
In Canada, federally regulated insurers answer to the Office of the Superintendent of Financial Institutions (OSFI). OSFI's guideline for working with outside vendors, called B-10, treats a cloud provider like any other key supplier. Insurers need a backup plan in case that provider fails, and contracts that say where their records are kept. OSFI must also be able to reach certain records when it asks. Provinces can add rules too. Quebec, for example, requires a privacy check before personal information leaves the province. So you can't pick just any cloud location.
Moving to the cloud doesn't move your regulatory duties. They travel with your data.
Moving decades of policy and claims data safely
Insurance data migration is where many projects slip. A life policy written in 1990 may still be active. A liability claim can stay open for years. All of that history has to move, stay readable, and still add up afterward.
Start by mapping old fields to new ones and fixing duplicates and gaps. Then reconcile the numbers that matter most: premiums, reserves, and claim payments must match between the old and new systems. Run both systems side by side for at least one full billing cycle, and compare the results before switching. Data pipelines that check every record as it moves make this repeatable.
Not every record needs to live in the new system. Closed policies and old claims can move to a low-cost archive that staff and auditors can still search. That keeps the new system lean while still meeting record-keeping rules.
A phased migration plan that keeps policies running
Start with an assessment. List every system, the data it holds, what connects to it, and which rules apply to it. A cloud readiness assessment turns that list into an order of moves and a realistic timeline.
Next, build a secure cloud foundation on AWS or Google Cloud. Encryption, access controls, logging, and multi-factor login should all be in place before any data arrives. Move low-risk workloads first, such as reports and archives, to prove the setup works.
Then move core systems one product line at a time, timing each cutover around renewal dates so customers never notice. Keep the old system running until the new one has passed a full cycle, then switch it off. Once the data finally lives in one place, insurers can add AI for claims and underwriting on top.
Conclusion
Insurance legacy modernization works best as a series of careful moves, not one giant leap. Move what's safe as-is, rebuild what changes often, and leave closed books alone. Plan around NYDFS, NAIC, and OSFI rules from day one, and prove every number before you switch off an old system. The hardest part is deciding the order. Bring us the list of your core systems, and we'll help you sort which ones to move first, which to rebuild, and which to leave in place.