Why patient data changes the rules for a CRM
A clinic's CRM holds more health data than most teams realize. Names, visit types, referral notes, call recordings, and form answers all end up there. That's why choosing a HIPAA compliant CRM matters as much as choosing the right electronic health record (EHR) system. Under HIPAA, the U.S. health privacy law, a patient's name linked to a visit, a test, or a bill is protected health information, or PHI.
Most CRMs were built for sales teams. They make it easy to copy data, export lists, connect apps, and share records across the company. Those same strengths turn into risks when the records belong to patients. One open export or one unapproved app can expose thousands of people.
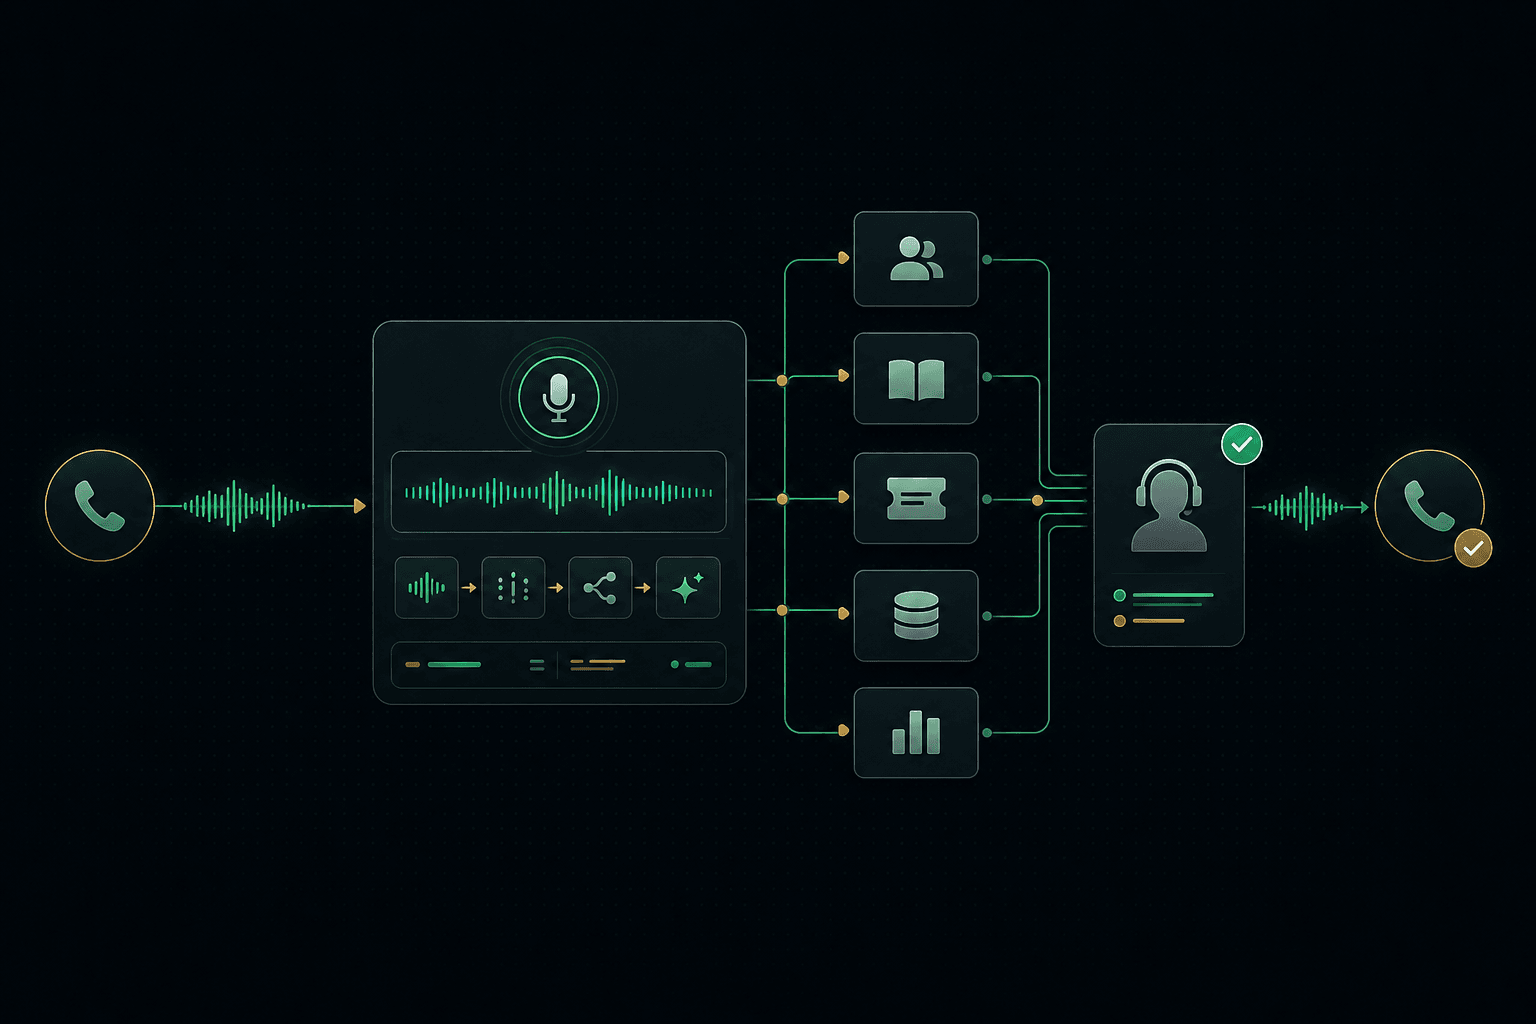
AI raises the stakes. A healthcare CRM with AI can summarize calls, draft replies, and flag patients who need a follow-up. Each of those steps sends patient data to an AI model. If that AI provider hasn't signed the right agreement, using it breaks HIPAA rules, even when everything else in the CRM is secure.
What makes a CRM HIPAA compliant
A HIPAA compliant CRM needs three things. The vendor signs a business associate agreement that covers every feature you use. The system protects patient data with access controls, encryption, and audit logs. And your team follows HIPAA rules in daily work. No software is compliant on its own, straight out of the box.
A business associate agreement, or BAA, is a contract in which a vendor that handles PHI promises to protect it the way HIPAA requires. Vendors often sign one only for certain products or plans. HubSpot, for example, signs a BAA only for Enterprise customers who turn on its sensitive data settings, and some of its tools stay outside it. So don't just ask whether a CRM is HIPAA compliant. Ask which of the features you plan to use the BAA actually covers.
Each safeguard has a plain meaning in a CRM and a clear question to ask before you sign.
Requirement | What it means in a CRM | What to ask the vendor |
BAA | The vendor agrees in writing to protect PHI | Which products, plans, and features does it cover? |
Access control | Each user sees only what their role needs | Can we limit access by role and by field? |
Audit controls | Every view, change, and export is recorded | Can we search, export, and keep the logs? |
Encryption | Data is unreadable without a key, stored or sent | Are backups and test copies encrypted too? |
Login security | Users prove who they are before they get in | Is multi-factor login built in and enforced? |
Backup and recovery | Data comes back after an outage or attack | How fast can we restore, and when was it last tested? |
These rules are getting stricter, too. The U.S. Department of Health and Human Services (HHS) has proposed making safeguards like encryption and multi-factor login firm requirements, so it's smart to build for them now.
Inside a HIPAA compliant AI CRM: data, access, and integrations
A HIPAA-compliant AI CRM works in layers, and each layer has one job. The data layer decides where PHI lives. It should run on cloud services covered by a BAA, such as the HIPAA-eligible services from AWS or Google Cloud. HHS guidance says any cloud provider storing patient data needs a BAA, even if the data is encrypted. One mistake to avoid is copying real patient records into a test version of the CRM, which rarely has the same protections. Use made-up sample data for testing instead.
The access layer decides who sees what. Front-desk staff need names and appointment times, not lab results. Billing needs insurance details, not clinical notes. Access by role and by field puts HIPAA's minimum necessary rule into practice, so each person sees only the data their job requires. Multi-factor login and automatic timeouts protect shared front-desk computers.
The integration layer connects the CRM to the EHR and other tools. EHR CRM integration usually runs through Fast Healthcare Interoperability Resources (FHIR), a common standard for sharing health data that most major EHR systems support. The CRM should pull only the fields it needs, like visit dates and the care team, not the full chart. Every connected app needs its own BAA too. If you're switching systems, plan this early. Migrating and cleaning up records from an older CRM is when PHI most often lands in the wrong place.
Audit logs that stand up to a HIPAA review
A HIPAA audit log is a record of who accessed patient data, what they did, and when. In a CRM, it should capture every view, edit, export, and deletion of PHI, along with logins and permission changes. The log must be protected from editing, kept as long as your policy requires, and reviewed on a regular schedule.
HIPAA requires audit controls but doesn't list exactly what to record. A good test: if a patient asks who looked at their record, you should be able to name the person, the record, and the time. The biggest risk is often inside the building, such as staff looking up a neighbor's or a coworker's record. Automated alerts can flag warning signs, like one user opening hundreds of records in an hour.
AI needs a place in the log too. When an AI agent reads a record to draft a reply, the log should name the agent, the task it ran, and the person who approved the result. And logs only protect patients when someone reads them, so reviews need an owner and a date.
Using AI with patient data safely
HIPAA allows AI to work with patient data when the AI provider signs a business associate agreement and the CRM sends data only to features it covers. The CRM should also share only what each task needs and stop the provider from training on your data. A person should review the AI's work before it reaches a patient.
Anthropic, OpenAI, and Amazon Bedrock all offer BAAs for business use, but each one leaves certain features out. Consumer chat apps are a different story. OpenAI's own HIPAA guide says its consumer ChatGPT plans aren't covered. So a staff member who pastes patient notes into a free chatbot creates a HIPAA problem. If an AI tool isn't covered by a BAA, patient data should never reach it.
A CRM's built-in AI needs the same check. Salesforce's BAA, for example, excludes some Einstein features and requires data masking for its Agentforce services. Masking swaps names and ID numbers for placeholders before text reaches the AI, so it can draft a follow-up without knowing who it's for. Teams that want full control over which AI sees which data often choose a custom AI CRM where you decide where patient data lives. It can be built to support SOC 2 and HIPAA from the start.
Turning compliance into a better patient experience
Compliance work often looks like pure cost. In a patient CRM, it also makes better service possible. The system knows what each patient agreed to and how they like to be contacted. Start with the difference between care messages and marketing. HHS says appointment reminders count as part of treatment, so they don't need written permission. Promotions for a new service usually count as marketing, and those do. A good patient CRM tags each message type and checks permission before anything goes out.
Contact preferences work the same way. HIPAA lets providers email patients with reasonable safeguards, and patients can ask to be reached another way. Storing each patient's preferred channel, language, and contact hours means messages arrive where people will actually see them. This is where HIPAA compliant patient communication pays off.
Trust follows. One complete patient view means people aren't asked the same questions at every step. Add patient outreach that helps cut no-shows, and patients start to feel the difference.
Patients rarely see your compliance work. They feel it every time the right message arrives at the right moment.
Conclusion
A HIPAA compliant CRM isn't something you buy with a label on the box. It's a BAA that covers the features you use, access limited by role, audit logs someone reviews, and AI that sees patient data only under the right agreement. Get those right, and compliance becomes the reason patients trust your reminders and answer your messages. The easiest way to begin is to list every place patient data enters, sits in, or leaves your CRM today. Walk through that list with us, and you'll know which safeguards are missing before any patient data reaches an AI model.